“What if someone gets into an account?”
Start with identities, email and the way information is shared. Review multi-factor authentication, permissions, phishing protection and the steps people take when a message feels wrong.

CYBER SECURITY / BUILT AROUND YOUR BUSINESS
Protect the work you do, the information you hold and the people who depend on you. Turn cyber risk into a plan you can understand and act on.
START WITH A REAL BUSINESS QUESTION
You don’t need to know the product names. Start with the concern, and we’ll help connect it to the right service.
Start with identities, email and the way information is shared. Review multi-factor authentication, permissions, phishing protection and the steps people take when a message feels wrong.
Review the devices and systems your protection can actually see. Connect the right signals with a process for investigating alerts, escalating concerns and approving response actions.
Use a targeted, authorised assessment to understand weaknesses in the systems that matter. Separate routine vulnerability checks from testing that validates whether a weakness can be exploited.
Bring backups, recovery priorities and incident responsibilities together. Check what can be restored, agree the order systems need to return and practise the decisions people may need to make.
ONE CONNECTED SECURITY PLAN
REDUCE EXPOSURE
Secure access, maintain supported systems and build sensible working habits around your information.
Strengthen protectionSEE WHAT MATTERS
Choose the visibility your environment needs and define who reviews the alerts.
Connect detectionMAKE ACTION CLEAR
Set decision makers, escalation routes, communications and containment permissions before an incident.
Build readinessGET WORK MOVING
Match protected data, restore checks and business priorities with a recovery plan people can follow.
Plan resilienceTEST THE DEFENCES THAT MATTER
A penetration test investigates exploitable weaknesses in an agreed scope. Adversary simulation explores how your defences and response stand up to an agreed attack scenario.
Networks, web applications, APIs, cloud environments and identity controls, scoped around your requirements.
Tabletop scenarios and collaborative exercises to practise decisions, communications and escalation.
Prioritised remediation, assigned owners and agreed follow-up or retesting.

Agree written permission, targets, exclusions, test windows, contacts and stop conditions before testing begins.
THE COLOURS OF CYBER SECURITY
From red and blue to collaborative exercises, choose an approach that answers a useful question for your business.
Test agreed attack paths and how defensive controls respond.
Improve monitoring, investigation and defensive operations.
Share attacker and defender findings to strengthen detection and response.
Consider security in architecture and software development.
Use offensive findings to inform developers and builders.
Bring defensive experience into engineering and delivery.
Set rules, oversee safety and evaluate the agreed exercise.
Team colours describe roles and ways of working; terminology varies between providers. We agree the objectives, participants and deliverables rather than relying on the label alone.
Little or no internal knowledge, to explore an external perspective.
Some agreed knowledge or access, to focus testing on realistic scenarios.
Detailed knowledge and access, for a more informed assessment of the agreed systems.

BE READY FOR THE DIFFICULT DAY
When systems are unavailable, people need clear decisions and a dependable starting point. Bring your IT response and business priorities into the same conversation.
SECURITY IN YOUR BUSINESS CONTEXT
CLIENT CONFIDENTIALITY
Sensitive records, trusted access and business-critical workflows need clear protection and ownership.
Explore sector prioritiesCONNECTED LEARNING
Support staff and learners with managed access, protected devices and recovery planning for teaching systems.
Explore education ITWORK ACROSS LOCATIONS
Connect protection and response across your agreed locations, users and shared business systems.
Explore multi-site ITA CLEARER FIRST CONVERSATION
Tell us what you rely on, what worries you and who manages security today. Your brief helps us identify a useful starting point.
Build my security briefSee the security service portfolioStart with your critical systems, identities, sensitive information and current protection. A discovery conversation helps identify immediate gaps and a manageable sequence of improvements.
Combine preventive controls, detection and response with recoverable backups and rehearsed recovery decisions. Backup alone does not prevent an attack; protection alone does not replace a recovery plan.
A test gives evidence about the agreed scope at a point in time. New changes, vulnerabilities and attack methods can introduce risk, so findings should feed into ongoing management.
We review what you already have before recommending changes. Product compatibility, visibility, licences and operational responsibilities determine what can be included.
EXPLORE THE SECURITY PORTFOLIO
Everyday protection with priorities, ownership and regular reviews.
Explore this serviceTurn security signals into a defined investigation and response.
Explore this serviceFind exploitable weaknesses and get a practical remediation plan.
Explore this serviceConnect security decisions, people and evidence.
Explore this serviceProtect computers, servers and the software they run.
Explore this serviceHelp protect accounts, messages and shared information.
Explore this serviceReview access, configuration and exposure across your cloud estate.
Explore this serviceDiscover weaknesses, prioritise changes and track resolution.
Explore this serviceTest realistic attack paths and improve defensive response.
Explore this servicePrepare your organisation for an independently assessed baseline.
Explore this serviceMake safer working habits easier to understand and practise.
Explore this servicePrepare decisions, communications and recovery before disruption.
Explore this serviceA CONTRACT YOU CAN UNDERSTAND
IT Mountain coordinates the agreed service. Specialist assessment or security operations may be delivered by an appointed provider. The proposal identifies responsibilities, access and the route to support.
Define supported users, devices and systems, monitoring hours, response commitments and approval points. Licences, testing, major changes and specialist recovery are itemised where separately scoped.
Keep findings, action owners and unresolved risks visible. Agree a review cadence so the service follows changes in your organisation rather than standing still.
Tell us what needs protecting and what a better service would look like.
TECHNOLOGY WITH A PURPOSE
Explore what each capability does and where it could help. We’ll confirm the selected technology, licensing, delivery team and support responsibilities in your proposal.
Connect device, network, email and detection controls.
Choose a combination of protection and managed operations around the systems your people use. Confirm the supported estate, licences, monitoring coverage and response authority together.
Protect devices and the business connections they rely on.
Review the boundaries around office networks, remote access and enrolled devices. Combine suitable controls with practical management and a clear route for investigating security findings.
Keep endpoint policies, protection and visibility in view.
Bring the protection of supported computers and servers into a manageable operating service. Agree policies, enrolment, updates and how detection findings are handled.
Strengthen device protection and connect it with a response service.
Start with the assets to protect, then define the operational work needed after an alert. The proposal identifies the selected protection, detection capabilities and any managed response coverage.
Protect the routes between sites, remote users and cloud workloads.
Design network security around the connections your business needs. Review firewall policies, remote access and cloud boundaries, with maintenance and change responsibilities clearly assigned.
Bring supported security signals into a more useful operating picture.
Connect information from supported devices and cloud workloads so investigations have better context. Coverage depends on the integrations, configuration and licences included in your service.
Control what runs and limit what permitted software can do.
Application allowlisting defines permitted software, while containment and privilege controls can limit its behaviour. Discovery, policy design and a workable approval process help protect productivity.
Investigate suspicious device and account activity with defined coverage.
Connect enrolled endpoints and supported identities with a managed investigation service. Agree the response capabilities, escalation route and the handover to ongoing IT support.
Connect endpoint insight with wider security context.
Give investigations access to supported endpoint and related security signals. Define the operating team and any specialist response service alongside the technology capabilities.
Build endpoint visibility around the coverage your organisation needs.
Select the supported endpoint and investigation capabilities that fit your estate. Enrolled assets, selected modules and the operational service determine the visibility and response available.
Connect endpoint investigations with cloud and identity activity.
Review threats across supported endpoints, accounts and cloud services. Scope the connected environments together, then agree containment permissions and the remediation handover.
Put an agreed operating service behind your security signals.
Combine detection, endpoint protection and exposure insight around clear operating responsibilities. Specialist investigation, customer communication and remediation each need an understood owner.
Turn supported endpoint alerts into triage and follow-up.
Connect supported endpoint technology with an agreed monitoring service. State the selected platform, enrolled assets and how investigation and response link to your ongoing IT support.
Get testing evidence and practical support for assurance requirements.
Use specialist testing to understand weaknesses in agreed networks, applications and cloud environments. Assessment scope, report deliverables and any independent certification route are confirmed for the engagement.
Explore weaknesses across the systems your business relies on.
Agree the targets, test perspective and deliverables before technical assessment begins. Findings should help your team understand the weakness, its impact and the route to remediation.
Get an objective view of your critical systems and configurations.
Choose assessments around the applications, infrastructure and cloud settings that matter to your organisation. Confirm the testing specialists, engagement credentials and reporting scope before delivery.
Explore the route an attacker could take and how your defences respond.
Define a realistic business objective, permitted techniques and the defensive response to evaluate. An exercise needs agreed rules, safety boundaries and clear learning outcomes.
Investigate exploitable weaknesses within an authorised scope.
Plan specialist assessment around agreed targets, test windows and business priorities. Reports explain evidence and remediation, with follow-up or retesting defined in the engagement.
Connect recurring assessment with reporting and remediation.
Build a testing rhythm around meaningful changes and the systems you need to assess. Agree engagement coverage, access to findings and how remediation is reviewed over time.
Bring security monitoring, testing and reporting into one practical plan.
Connect several security activities around a shared view of your business. Your scope defines the monitored systems, specialist delivery, reporting and the handover to your IT support.
Find gaps across networks and applications, then plan improvements.
Use targeted assessment to understand where your business is exposed. The engagement sets out the systems to review, the evidence to collect and the actions your team can take after the findings.
Add specialist security skills where your business needs them.
Build specialist assessments and protection into your wider IT plan. Agree which experts deliver the work, how results are communicated and who owns the next improvements.
Understand technical exposure and prepare the evidence for assessment.
Connect testing and exposure reviews with the controls your organisation needs to demonstrate. Certification support prepares you for the agreed assessment; certification is awarded independently.
Capabilities are selected and scoped for your environment. Your agreement identifies the appointed technology and delivery providers before the service begins.
A CONNECTED SECURITY PROGRAMME
Security spans the people, accounts, devices and systems your business relies on. Build a practical combination of controls, technology and operational support around your risks, with clear responsibilities for maintaining it.
Protect the accounts that unlock your business. Review multi-factor authentication, conditional access, single sign-on and role-based permissions. Separate administrator accounts and make joiner, mover and leaver processes part of everyday security.
Explore this areaBring laptops, desktops, servers and supported mobile devices into view. Combine endpoint detection and response with patching, disk encryption, application controls and device compliance. Agree who can investigate an alert or isolate a compromised device.
Explore this areaReduce exposure to malicious attachments, unsafe links and impersonation. Review email filtering, domain authentication and mailbox access alongside staff reporting and phishing awareness. Help teams recognise unexpected payment requests and verify them through a trusted route.
Explore this areaReview firewalls, remote access and the boundaries between business systems. Use segmentation to limit unnecessary connections, with secure VPN or zero-trust access options selected for your environment. Include DNS and web filtering where suitable.
Explore this areaConnect supported endpoint, identity, email and cloud signals so suspicious activity can be investigated in context. Define alert triage, escalation, authorised containment and reporting. Select monitoring hours and response commitments around your business requirements.
Explore this areaReview cloud configuration, sharing permissions and access to sensitive information. Consider data classification, data loss prevention and logging alongside Microsoft 365 and other supported platforms. Track configuration changes and the responsibilities shared with your cloud providers.
Explore this areaBuild an inventory, identify weaknesses and prioritise fixes by business impact and exposure. Combine routine vulnerability reviews with authorised penetration testing where appropriate. Assign remediation owners and use retesting to check that agreed improvements work.
Explore this areaBring preventive controls, detection and business continuity into one plan. Review isolated or immutable backup options, restrict backup administration and test restoration. Rehearse who makes decisions, how people communicate and which systems need to return first.
Explore this areaTECHNOLOGY IN CONTEXT
EDR investigates activity on endpoints. XDR brings together supported signals across several security layers. MDR adds a managed service for investigation and response. Coverage, integrations and authorised actions determine how these capabilities work together.
A SIEM collects and analyses security logs from connected systems. SOAR capabilities help orchestrate agreed workflows and response tasks. Useful outcomes depend on reliable data, meaningful detection rules, tested playbooks and people with clear decision-making authority.
For suitable Microsoft environments, options can include Defender XDR for connected detection, Microsoft Sentinel for SIEM and SOAR, and Entra Conditional Access for access policies. Product selection, licensing, integrations and delivery scope are confirmed in your proposal.
Microsoft technology overview ↗These are technology options for discussion. The agreed service identifies the products, supported systems, delivery providers and coverage included.
WHEN SOMETHING NEEDS ATTENTION
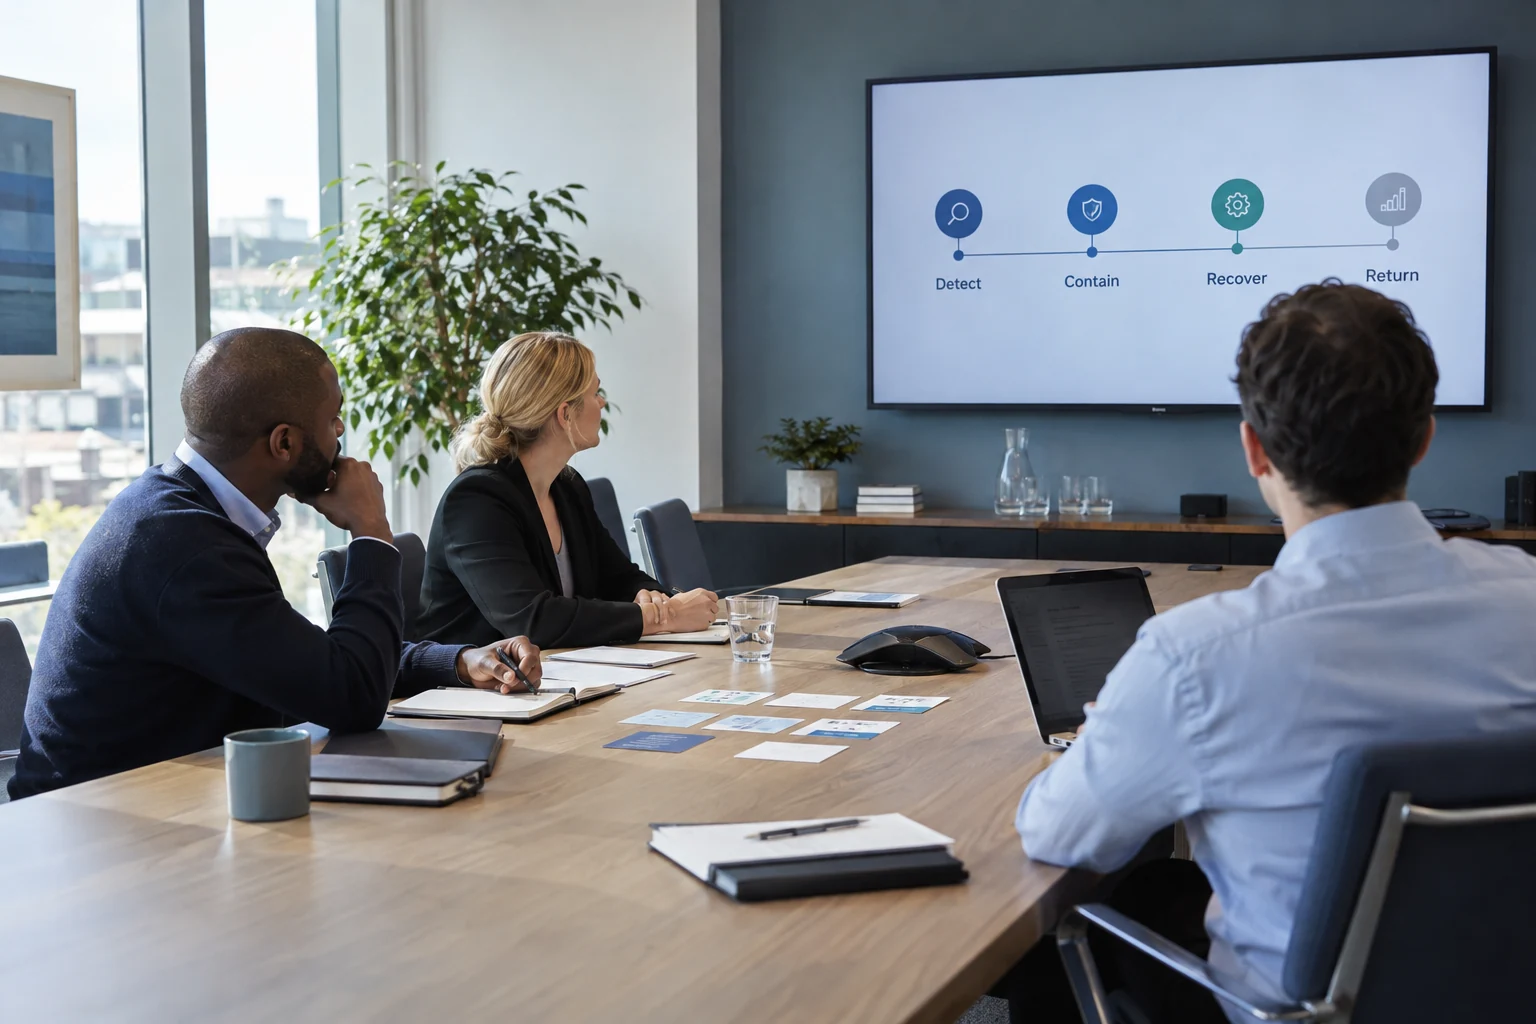
Validate the alert, establish the affected accounts or systems and assess business impact.
Follow agreed authority to limit exposure, such as isolating a device or restricting an account.
Coordinate remediation and restoration with business priorities and the agreed recovery plan.
Record lessons, update controls and track corrective actions with named owners.
Bring your current tools, concerns and business priorities. We’ll help shape the next steps.
Discuss your security requirements ↗Explore practical preparation guidance from the National Cyber Security Centre.