Network assurance
Assess agreed internal, external and wireless targets.
AUTHORISED TESTING / IT MOUNTAIN
Understand how an attacker could affect your business, then give your team a practical way to close the gaps. Scope the right test, agree the rules and turn technical findings into business priorities.

YOUR NEXT BUSINESS STEP
Prepare for a launch, customer assurance review or infrastructure change with authorised testing that turns technical findings into a practical remediation plan.
Assess agreed internal, external and wireless targets.
Explore authentication, access controls and application attack paths.
Check agreed fixes and make the remaining priorities clear.
Share the targets, ownership, preferred test window and any assurance deadline.
SCOPE THE SYSTEMS THAT MATTER
An expert-led penetration test investigates whether weaknesses can be exploited within an authorised scope. It complements ongoing vulnerability management rather than replacing it.
Assess agreed internet-facing assets, internal networks, segmentation and attack paths between systems.
Review scoped cloud configurations, identities and exploitable access paths. Provider permissions are confirmed first.
Explore this serviceExamine authentication, authorisation, data handling and application workflows in the agreed environment.
Test selected wireless networks, access arrangements and boundaries between users and resources.
Explore realistic objectives and improve how defenders identify and handle agreed attack techniques.
Explore this serviceReview agreed configurations and verify remediation against the original findings and retest scope.
Explore this serviceTHE RIGHT LEVEL OF KNOWLEDGE
Little prior knowledge is supplied. This can help explore what is visible or accessible to an outsider within agreed targets and time. It is not automatically the deepest assessment.
Provide selected credentials or system knowledge to focus testing on relevant workflows, user roles or an agreed attack scenario.
Provide architecture, configuration, source code or administrative access where appropriate, to enable a more informed review within the agreed scope.
FINDINGS YOUR TEAM CAN USE
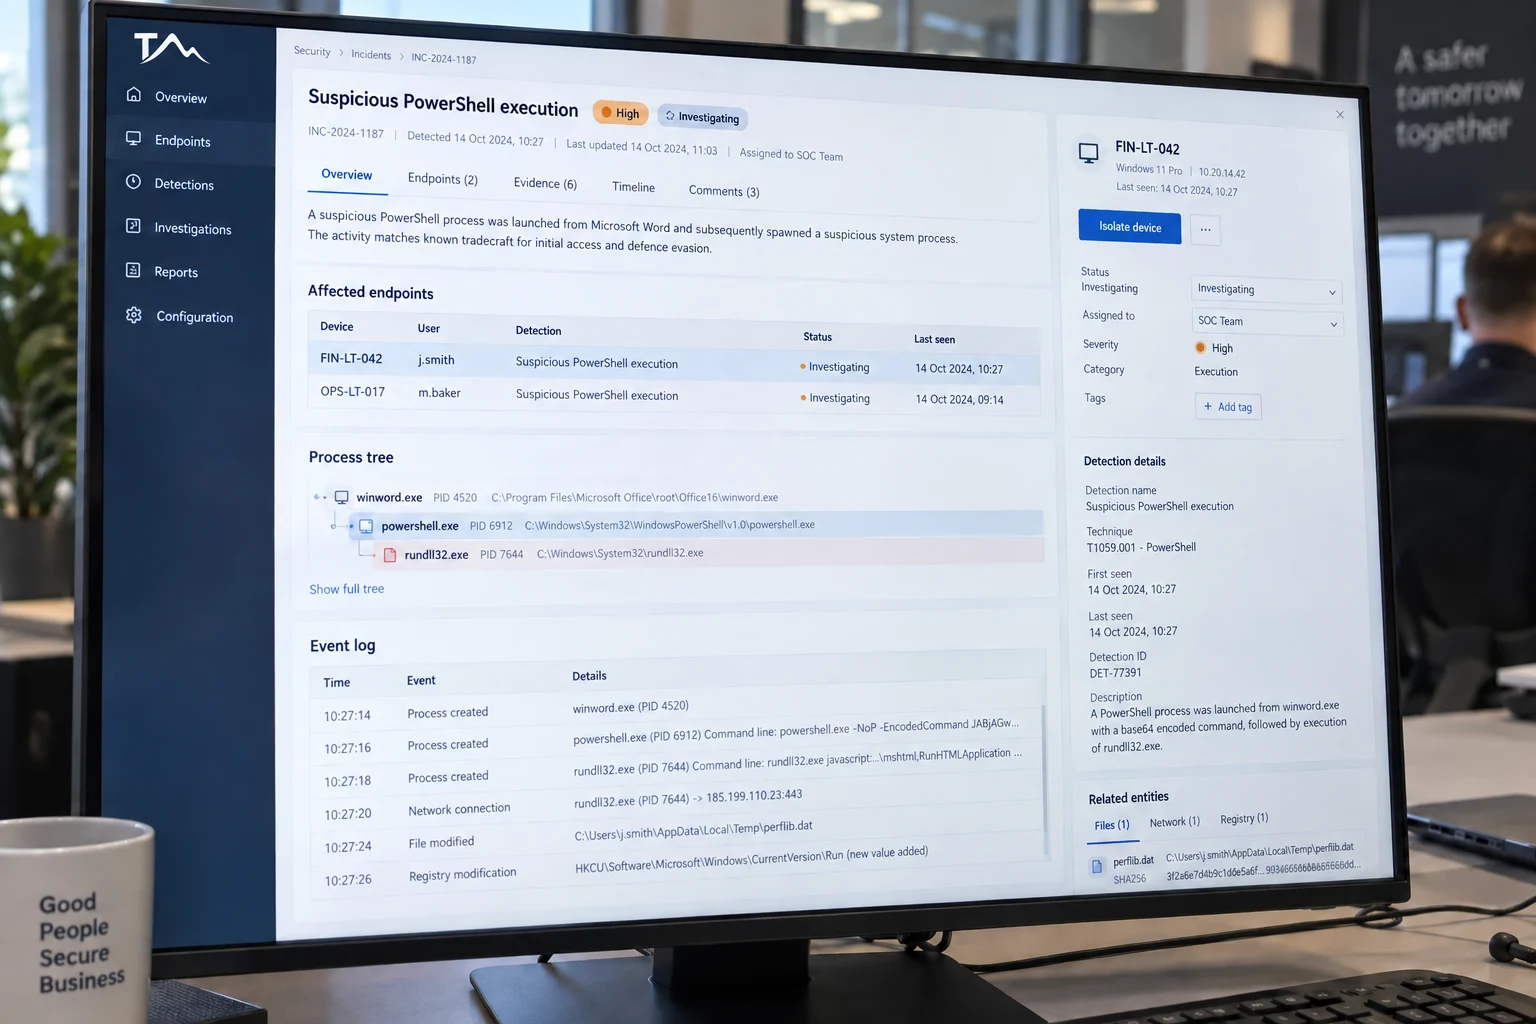
A report should help both your technical team and the people deciding what happens next. Agree the deliverables and reporting format before the engagement begins.
Summarise the tested scope, business exposure and the limitations of the engagement.
Explain validated findings, affected assets, risk ratings and practical remediation guidance.
Discuss the findings, assign owners and agree whether follow-up testing is required.
A PLANNED START
Record objectives, targets, exclusions, test windows and delivery requirements.
Confirm permission, safe handling, contacts and stop conditions.
Perform the agreed assessment and communicate material findings.
Prioritise remediation, debrief the team and agree any retest.
A CONTRACT YOU CAN UNDERSTAND
IT Mountain coordinates the agreed service. Specialist assessment or security operations may be delivered by an appointed provider. The proposal identifies responsibilities, access and the route to support.
Define supported users, devices and systems, monitoring hours, response commitments and approval points. Licences, testing, major changes and specialist recovery are itemised where separately scoped.
Keep findings, action owners and unresolved risks visible. Agree a review cadence so the service follows changes in your organisation rather than standing still.
Tell us what needs protecting and what a better service would look like.
TECHNOLOGY WITH A PURPOSE
Explore what each capability does and where it could help. We’ll confirm the selected technology, licensing, delivery team and support responsibilities in your proposal.
Get testing evidence and practical support for assurance requirements.
Use specialist testing to understand weaknesses in agreed networks, applications and cloud environments. Assessment scope, report deliverables and any independent certification route are confirmed for the engagement.
Explore weaknesses across the systems your business relies on.
Agree the targets, test perspective and deliverables before technical assessment begins. Findings should help your team understand the weakness, its impact and the route to remediation.
Get an objective view of your critical systems and configurations.
Choose assessments around the applications, infrastructure and cloud settings that matter to your organisation. Confirm the testing specialists, engagement credentials and reporting scope before delivery.
Explore the route an attacker could take and how your defences respond.
Define a realistic business objective, permitted techniques and the defensive response to evaluate. An exercise needs agreed rules, safety boundaries and clear learning outcomes.
Investigate exploitable weaknesses within an authorised scope.
Plan specialist assessment around agreed targets, test windows and business priorities. Reports explain evidence and remediation, with follow-up or retesting defined in the engagement.
Connect recurring assessment with reporting and remediation.
Build a testing rhythm around meaningful changes and the systems you need to assess. Agree engagement coverage, access to findings and how remediation is reviewed over time.
Bring security monitoring, testing and reporting into one practical plan.
Connect several security activities around a shared view of your business. Your scope defines the monitored systems, specialist delivery, reporting and the handover to your IT support.
Find gaps across networks and applications, then plan improvements.
Use targeted assessment to understand where your business is exposed. The engagement sets out the systems to review, the evidence to collect and the actions your team can take after the findings.
Add specialist security skills where your business needs them.
Build specialist assessments and protection into your wider IT plan. Agree which experts deliver the work, how results are communicated and who owns the next improvements.
Understand technical exposure and prepare the evidence for assessment.
Connect testing and exposure reviews with the controls your organisation needs to demonstrate. Certification support prepares you for the agreed assessment; certification is awarded independently.
Capabilities are selected and scoped for your environment. Your agreement identifies the appointed technology and delivery providers before the service begins.
YOUR QUESTIONS
No. Scanning helps identify potential weaknesses across assets. Penetration testing uses expert-led investigation to validate exploitable weaknesses in a defined scope. Each has a different purpose.
Testing can affect availability or data, depending on the techniques and environment. The rules of engagement set exclusions, test windows, emergency contacts and stop conditions. A staging environment may be appropriate for some work.
The scope can define little prior knowledge, selected credentials or detailed access to systems and documentation. The approach should match the question the test needs to answer.
Tell us any procurement or assurance requirement during discovery. The proposal identifies the appointed testing provider and relevant credentials; their accreditation is not presented as IT Mountain’s own.
The engagement sets out report delivery, debrief, remediation responsibilities and any included retest window. Major remediation projects and additional testing are separately agreed.