Identity & permissions
Review privileged accounts, service identities, role assignments and access paths in the agreed cloud estate.
SPECIALIST SECURITY / IT MOUNTAIN
Understand who can access your cloud systems, how they are configured and what happens when something changes. Shape security around your workloads and business dependencies.
THE SERVICE IN PRACTICE
Choose the activities that address your actual risks. Your service schedule confirms the supported estate, deliverables and responsibilities.
Review privileged accounts, service identities, role assignments and access paths in the agreed cloud estate.
Assess public access, network boundaries, logging and selected workload settings.
Confirm which platform signals can be collected, retained and connected to your operational service.
Review protected information, backup responsibilities and recovery dependencies alongside security controls.
BUILT AROUND YOUR BUSINESS
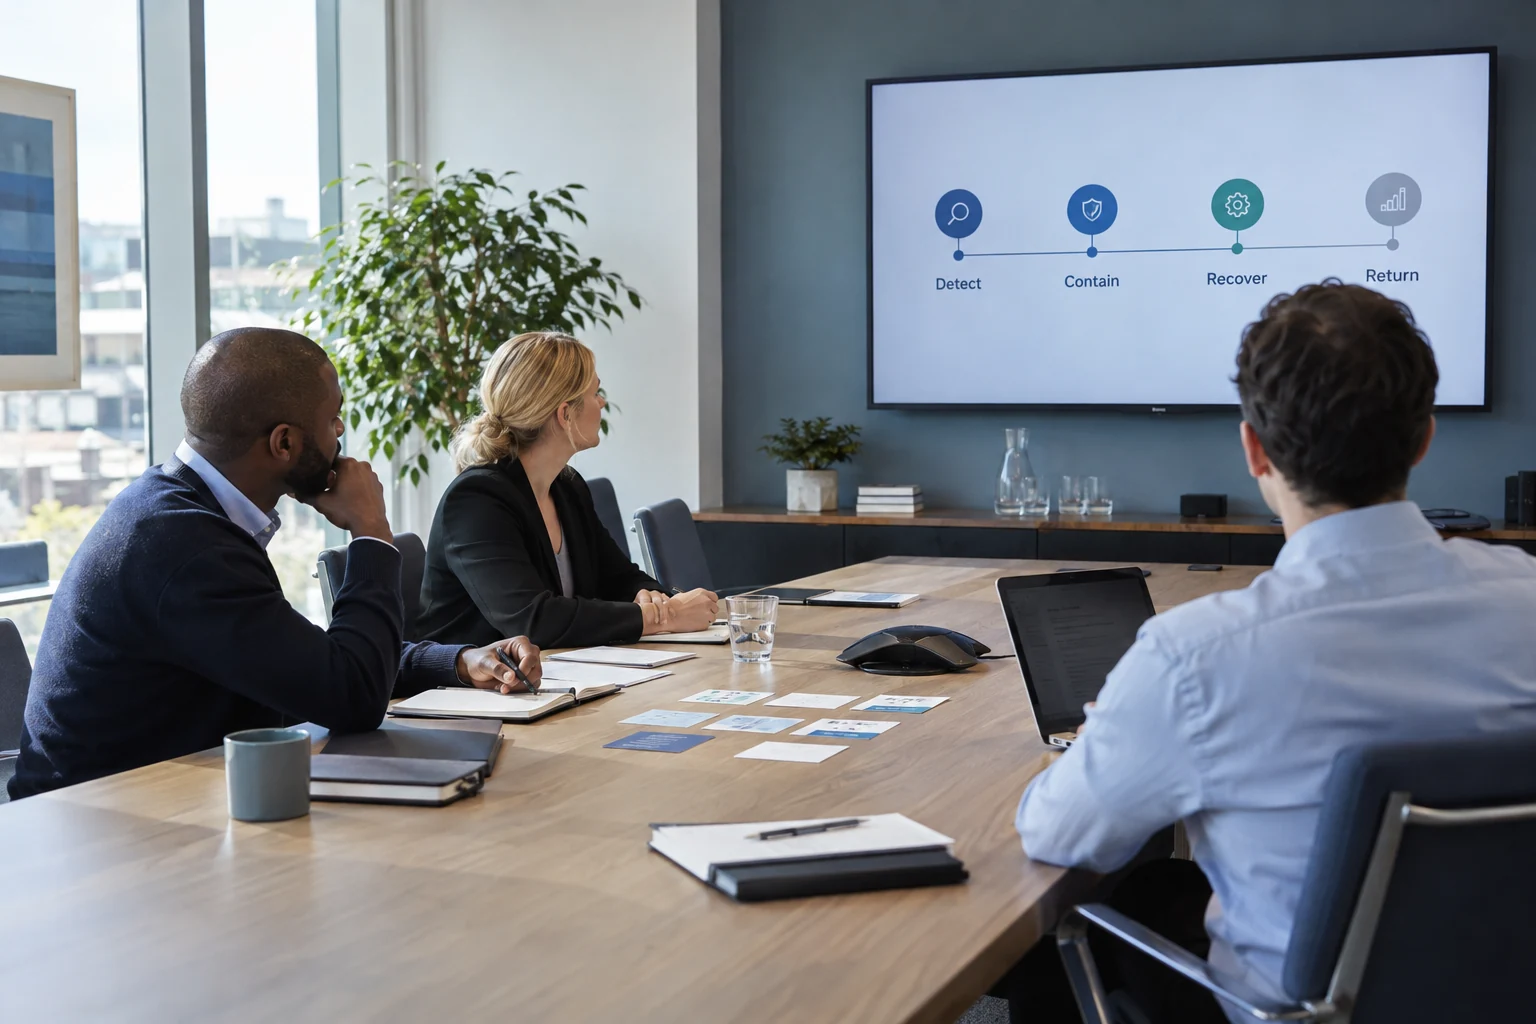
Start with the concern you want to address. Then agree the systems, people and evidence that belong in scope, including any specialist delivery needed.
Record accounts, workloads, ownership and critical data.
Review agreed configurations and exposure against your requirements.
Prioritise changes with business owners and test them safely.
A PLANNED START
Record accounts, workloads, ownership and critical data.
Review agreed configurations and exposure against your requirements.
Prioritise changes with business owners and test them safely.
Keep access, new workloads and exceptions visible over time.
A CONTRACT YOU CAN UNDERSTAND
IT Mountain coordinates the agreed service. Specialist assessment or security operations may be delivered by an appointed provider. The proposal identifies responsibilities, access and the route to support.
Define supported users, devices and systems, monitoring hours, response commitments and approval points. Licences, testing, major changes and specialist recovery are itemised where separately scoped.
Keep findings, action owners and unresolved risks visible. Agree a review cadence so the service follows changes in your organisation rather than standing still.
Tell us what needs protecting and what a better service would look like.
TECHNOLOGY WITH A PURPOSE
Explore what each capability does and where it could help. We’ll confirm the selected technology, licensing, delivery team and support responsibilities in your proposal.
Connect device, network, email and detection controls.
Choose a combination of protection and managed operations around the systems your people use. Confirm the supported estate, licences, monitoring coverage and response authority together.
Protect devices and the business connections they rely on.
Review the boundaries around office networks, remote access and enrolled devices. Combine suitable controls with practical management and a clear route for investigating security findings.
Protect the routes between sites, remote users and cloud workloads.
Design network security around the connections your business needs. Review firewall policies, remote access and cloud boundaries, with maintenance and change responsibilities clearly assigned.
Bring supported security signals into a more useful operating picture.
Connect information from supported devices and cloud workloads so investigations have better context. Coverage depends on the integrations, configuration and licences included in your service.
Capabilities are selected and scoped for your environment. Your agreement identifies the appointed technology and delivery providers before the service begins.
YOUR QUESTIONS
Responsibility is shared and varies by service. Your provider operates parts of the platform, while account access, data, configuration or workloads can remain your responsibility. Discovery maps those boundaries.
A configuration assessment examines agreed settings and controls. A penetration test investigates exploitable weaknesses under an authorised scope. Either or both may be appropriate.
Tell us about your infrastructure and workplace platforms during discovery. Supported environments, access requirements and specialist delivery are confirmed before the engagement.